
说明
本文是个人学习用的非官方中英对照译文,原文:https://diveintosystems.org/book/C9-ARM64/basics.html。
原书采用 CC BY-NC-ND 4.0 许可(禁止演绎),请勿公开传播本译文。
标为「译注」「现代更新」的内容是译者补充,不代表原书作者观点;代码与原文逐字一致,未作改动。
9.1. Diving into Assembly: Basics
为了初步了解汇编,我们修改汇编入门章节中的 adder 函数,简化它的行为。修改后的函数(adder2)如下:
For a first look at assembly, we modify the
adderfunction from the assembly introduction chapter to simplify its behavior. The modified function (adder2) is shown here:
1 | #include <stdio.h> |
要编译这段代码,使用以下命令:
To compile this code, use the following command:
1 | $ gcc -o adder adder.c |
接下来,用 objdump 命令查看这段代码对应的汇编:
Next, let’s view the corresponding assembly of this code by using the
objdumpcommand:
1 | $ objdump -d adder > output |
用 less 查看文件 output 时,输入 /adder 搜索与 adder2 相关的代码片段。与 adder 相关的部分应该类似下面这样:
Search for the code snippet associated with
adder2by typing/adderwhile examining the fileoutputusingless. The section associated withaddershould look similar to the following:
adder2 函数的汇编输出
Assembly output for the
adder2function
1 | 0000000000000724 <adder2>: |
如果你还不明白这是怎么回事,不必担心。我们会在后面的小节中更详细地介绍汇编。目前,我们先来研究一下这些单独指令的结构。
Don’t worry if you don’t understand what’s going on just yet. We will cover assembly in greater detail in future sections. For now, let’s study the structure of these individual instructions.
上例中的每一行都包含一条指令在程序内存中的 64 位地址(为节省空间,只保留最低三位数字)、与这条指令对应的字节,以及指令本身的文本表示。例如,d10043ff 是指令 sub sp, sp, #0x10 的机器码表示,这条指令位于代码段内存中的地址 0x724 处。注意,0x724 是与 sub sp, sp #0x10 指令相关的完整 64 位地址的缩写;为了便于阅读,objdump 省略了前导零。
Each line in the preceding example contains the instruction’s 64-bit address in program memory (shortened to the lowest three digits to save space), the bytes corresponding to the instruction, and the plain-text representation of the instruction itself. For example,
d10043ffis the machine code representation of the instructionsub sp, sp, #0x10, and the instruction occurs at address0x724in code memory. Note that0x724is an abbreviation of the full 64-bit address associated with thesub sp, sp #0x10instruction;objdumpomits the leading zeros to help with readability.
译注
A64 的每条指令都固定为 4 字节,所以清单中的地址每行恰好加 4(0x724、0x728、0x72c……),这与 x86 的变长指令形成鲜明对比。
要注意,一行 C 代码常常会被翻译成多条汇编指令。运算 a + 2 由代码段内存地址 0x728 到 0x730 处的三条指令表示:str w0, [sp, #12]、ldr w0, [sp, #12] 和 add w0, w0, #0x2。
It is important to note that a single line of C code often translates to multiple instructions in assembly. The operation
a + 2is represented by the three instructions at code memory addresses0x728through0x730:str w0, [sp, #12],ldr w0, [sp, #12], andadd w0, w0, #0x2.
原书警示 · 你的汇编可能看起来不一样!(Your assembly may look different!)
如果你一边读一边跟着编译代码,可能会注意到你得到的一些汇编示例与书中的不同。编译器输出的确切汇编指令,取决于生成它的编译器的版本、具体的体系结构以及底层的操作系统。本章的大多数汇编示例是在运行 64 位 Ubuntu Mate 操作系统的树莓派 3B+ 上用 GCC 生成的。如果你使用不同的操作系统、不同的编译器,或者不同的树莓派或单板计算机,你得到的汇编输出可能会有所不同。
在接下来的示例中,我们不使用任何优化选项。例如,编译任何示例文件(如 example.c)都使用命令 gcc -o example example.c。因此,接下来的示例中会有许多看似多余的指令。记住,编译器并不「聪明」——它只是遵循一系列规则,把人类可读的代码翻译成机器语言。在这个翻译过程中,出现一些冗余并不罕见。优化编译器在优化过程中会去掉许多这样的冗余,我们会在后面的章节中介绍优化。
If you are compiling your code along with us, you may notice that some of your assembly examples look different. The precise assembly instructions that are output by a compiler depend on the generating compiler’s version, the precise architecture, and the underlying operating system. Most of the assembly examples in this chapter were generated on a Raspberry Pi 3B+ running the 64-bit Ubuntu Mate operating system and using GCC. If you use a different operating system, a different compiler, or a different Raspberry Pi or single-board computer, your assembly output may vary.
In the examples that follow, we do not use any optimization flags. For example, we compile any example file (e.g.
example.c) using the commandgcc -o example example.c. Consequently, there are many seemingly redundant instructions in the examples that follow. Remember that the compiler is not “smart” — it simply follows a series of rules to translate human-readable code into machine language. During this translation process, it is not uncommon for some redundancy to occur. Optimizing compilers remove many of these redundancies during optimization, which is covered in a later chapter.
9.1.1. 寄存器
9.1.1. Registers
回想一下,寄存器是直接位于 CPU 上的、字大小的存储单元。ARMv8 CPU 共有 31 个用于存储 64 位通用数据的寄存器:x0 到 x30。尽管程序可能会把寄存器的内容解释为整数或地址,但寄存器本身并不加以区分。程序可以读写全部 31 个寄存器。
Recall that a register is a word-sized storage unit located directly on the CPU. The ARMv8 CPU has a total of 31 registers for storing general-purpose 64-bit data:
x0tox30. Whereas a program may interpret a register’s contents as integers or as addresses, the register itself makes no distinction. Programs can read from or write to all 31 registers.
ARMv8-A ISA 还规定了一些专用寄存器。首先值得注意的两个是栈指针寄存器(sp)和程序计数器寄存器(pc)。编译器把 sp 寄存器保留给维护程序栈布局的操作。pc 寄存器指向 CPU 要执行的下一条指令;与其他寄存器不同,程序不能直接写 pc 寄存器。其次,零寄存器 zr 永远存放值 0,只在作为源寄存器时有用。
The ARMv8-A ISA also specifies special-purpose registers. The first two worth noting are the stack pointer register (
sp) and the program counter register (pc). The compiler reserves thespregister for maintaining the layout of the program stack. Thepcregister points to the next instruction to be executed by the CPU; unlike the other registers, programs cannot write directly to thepcregister. Next, the zero registerzrpermanently stores the value 0, and is only useful as a source register.
译注 · 零寄存器
在汇编中零寄存器写作 xzr(64 位)或 wzr(32 位)。它也可以出现在目标位置,写入的结果会被直接丢弃:例如比较指令 cmp x0, x1 实际上就是 subs xzr, x0, x1(只要标志位、扔掉差值)。译者用 Clang 汇编这两条指令,得到的机器码完全相同(eb01001f)。
9.1.2. 寄存器的进阶记法
9.1.2. Advanced Register Notation
由于 ARMv8-A 是 32 位 ARMv7-A 体系结构的扩展,A64 ISA 提供了访问每个通用寄存器低 32 位的机制,即 w0 到 w30。图 1 展示了寄存器 x0 的一个示例布局。如果把 32 位数据存到组成部分寄存器 w0 中,寄存器的高 32 位就无法访问,并且会被清零。
Since ARMv8-A is an extension of the 32-bit ARMv7-A architecture, the A64 ISA provides mechanisms to access the lower 32 bits of each of the general-purpose registers, or
w0throughw30. Figure 1 shows a sample layout of registerx0. If 32-bit data is stored in component registerw0, then the upper 32 bits of the register become inaccessible, and are zeroed out.
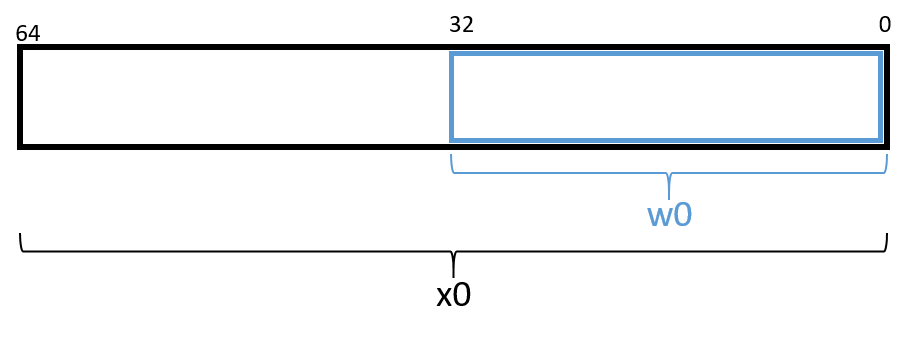
图 1. 寄存器 %x0 的组成部分寄存器布局
Figure 1. Component register layout of register %x0.
原书警示 · 编译器可能会根据类型选用寄存器的组成部分(The compiler may choose component registers depending on type)
阅读汇编代码时要记住,编译器在处理 64 位值(例如指针或 long 类型)时通常使用 64 位寄存器,在处理 32 位类型(例如 int)时则使用 32 位的组成部分寄存器。在 A64 中,32 位的组成部分寄存器与完整的 64 位寄存器混合使用是非常常见的。例如,在前面的 adder2 函数中,编译器引用的是组成部分寄存器 w0 而不是 x0,因为在 64 位系统上 int 类型通常占 32 位(四个字节)。如果 adder2 函数的参数是 long 而不是 int,编译器就会把 a 存放在寄存器 x0 而不是组成部分寄存器 w0 中。
When reading assembly code, keep in mind that the compiler typically uses the 64-bit registers when dealing with 64-bit values (e.g., pointers or
longtypes) and the 32-bit component registers when dealing with 32-bit types (e.g.,int). In A64, it is very common to see 32-bit component registers intermixed with the full 64-bit registers. For example, in theadder2function shown earlier, the compiler references component registerw0instead ofx0given thatinttypes typically take up 32 bits (four bytes) of space on 64-bit systems. If theadder2function had alongparameter instead of anintparameter, the compiler would storeain registerx0instead of component registerw0.
对于之前熟悉 A32 ISA 的读者,需要注意 A32 ISA 中的 32 位通用寄存器 r0 到 r12 映射到 A64 的组成部分寄存器 w0 到 w12。A64 ISA 可用的寄存器数量是原来的两倍多。
For readers previously familiar with the A32 ISA, it is important to note that the 32-bit general-purpose registers
r0tor12from the A32 ISA map to the A64 component registersw0tow12. The A64 ISA more than doubles the number of available registers.
9.1.3. 指令的结构
9.1.3. Instruction Structure
每条指令由一个指明它做什么的操作码(opcode)和一个或多个告诉指令如何去做的操作数(operand)组成。大多数 A64 指令通常采用下面的格式:
Each instruction consists of an operation code (or opcode) that specifies what it does, and one or more operands that tells the instruction how to do it. For most A64 instructions, the following format is typically used:
1 | opcode D, O1, O2 |
其中 opcode 是操作码,D 是目标寄存器,O1 是第一个操作数,O2 是第二个操作数。例如,指令 add w0, w0, #0x2 的操作码是 add,目标寄存器是 w0,两个操作数是 w0 和 #0x2。操作数有多种类型:
Where
opcodeis the operation code,Dis the destination register,O1is the first operand, andO2the second operand. For example, the instructionadd w0, w0, #0x2has the opcodeadd, a destination register ofw0, and the two operandsw0and#0x2. There are multiple types of operands:
译注
注意 ARM 汇编的目标在前(add D, O1, O2),与第 7、8 章 x86 的 AT&T 语法(目标在后)正好相反。
- 常数(字面量)值前面带有
#符号。例如,在指令add w0, w0, #0x2中,操作数#0x2是一个字面值,对应于十六进制值 0x2。
- Constant (literal) values are preceded by the
#sign. For example, in the instructionadd w0, w0, #0x2, the operand#0x2is a literal value that corresponds to the hexadecimal value 0x2.
- 寄存器形式指单个寄存器。指令
add sp, sp, #0x10用栈指针寄存器sp来指定目标寄存器,以及add指令所需两个操作数中的第一个。
- Register forms refer to individual registers. The instruction
add sp, sp, #0x10uses the stack pointer registerspto designate the destination register and the first of the two operands needed for theaddinstruction.
- 内存形式对应于主存(RAM)中的某个值,常用于地址查找。内存地址形式可以包含寄存器和常数值的组合。例如,在指令
str w0, [sp, #12]中,操作数[sp, #12]就是内存形式的一个例子。它大致可以翻译为:「把 12 加到寄存器sp中的值上,然后对得到的地址执行一次内存查找」。如果这听起来像是指针解引用,那是因为它就是!
- Memory forms correspond to some value inside main memory (RAM) and are commonly used for address lookups. Memory address forms can contain a combination of registers and constant values. For example, in the instruction
str w0, [sp, #12], the operand[sp, #12]is an example of a memory form. It loosely translates to “add 12 to the value in registersp, and then perform a memory lookup on the corresponding address.” If this sounds like a pointer dereference, that’s because it is!
9.1.4. 一个关于操作数的例子
9.1.4. An Example with Operands
详细解释操作数的最好方式是举一个简短的例子。假设内存中包含以下值:
The best way to explain operands in detail is to present a quick example. Suppose that memory contains the following values:
| 地址 | 值 |
|---|---|
| 0x804 | 0xCA |
| 0x808 | 0xFD |
| 0x80c | 0x12 |
| 0x810 | 0x1E |
Address Value 0x804 0xCA 0x808 0xFD 0x80c 0x12 0x810 0x1E
我们再假设下面这些寄存器中存放着所示的值:
Let’s also assume that the following registers contain the values:
| 寄存器 | 值 |
|---|---|
x0 |
0x804 |
x1 |
0xC |
x2 |
0x2 |
w3 |
0x4 |
Register Value x00x804 x10xC x20x2 w30x4
那么,表 1 中的操作数会求值为表中所示的值。表中的每一行把一个操作数与它的形式(例如常数、寄存器、内存)、它的含义以及它的值对应起来。
Then the operands in Table 1 evaluate to the values shown there. Each row of the table matches an operand with its form (e.g., constant, register, memory), how it is translated, and its value.
表 1. 操作数示例
Table 1. Example Operands
| 操作数 | 形式 | 含义 | 值 |
|---|---|---|---|
x0 |
寄存器 | x0 |
0x804 |
[x0] |
内存 | *(0x804) | 0xCA |
#0x804 |
常数 | 0x804 | 0x804 |
[x0, #8] |
内存 | *(x0 + 8) 即 *(0x80c) |
0x12 |
[x0, x1] |
内存 | *(x0 + x1) 即 *(0x810) |
0x1E |
[x0, w3, SXTW] |
(符号扩展)内存 | *(x0 + SignExtend(w3)) 即 *(0x808) |
0xFD |
[x0, x2, LSL, #2] |
带比例的内存 | *(x0 + (x2 << 2)) 即 *(0x80c) |
0x12 |
[x0, w3, SXTW, #1] |
(符号扩展)带比例的内存 | *(x0 + SignExtend(w3 << 1)) 即 *(0x80c) |
0x12 |
Operand Form Translation Value x0Register x00x804 [x0]Memory *(0x804) 0xCA #0x804Constant 0x804 0x804 [x0, #8]Memory *( x0+ 8) or *(0x80c)0x12 [x0, x1]Memory *( x0+x1) or *(0x810)0x1E [x0, w3, SXTW](Sign-Extend) Memory *( x0+ SignExtend(w3)) or *(0x808)0xFD [x0, x2, LSL, #2]Scaled Memory *( x0+ (x2 << 2)) or *(0x80c)0x12 [x0, w3, SXTW, #1](Sign-Extend) Scaled Memory *( x0+ SignExtend(w3 << 1)) or *(0x80c)0x12
译注 · 表中两处写法
- 实际汇编语法中移位说明符与移位量之间没有逗号:应写作
[x0, x2, lsl #2]、[x0, w3, sxtw #1]。译者用 Clang 汇编ldr w1, [x0, x2, lsl, #2]会报错,去掉逗号后通过。 - 寄存器偏移的移位量不能随意选:它只能是 0 或「访问宽度的 log₂」。所以
ldr w1, [x0, w3, sxtw #1](4 字节加载配#1)会被汇编器拒绝,只有 2 字节加载ldrh w1, [x0, w3, sxtw #1]才合法;4 字节加载只能用#2(或不移位)。表中按「w3左移 1 位」算出的 0x80c 只是演示寻址计算。
在表 1 中,记号 x0 表示 64 位寄存器 x0 中存放的值,而 w3 表示组成部分寄存器 w3 中存放的 32 位值。操作数 [x0] 表示应当把 x0 中的值当作一个地址,并对它解引用(查找该地址处的值)。因此,操作数 [x0] 对应于 *(0x804),即值 0xCA。可以用字的符号扩展(SXTW)指令把对 32 位寄存器的操作与 64 位寄存器结合起来。所以,[x0, w3, SXTW] 先把 w3 符号扩展为 64 位值,再把它加到 x0 上并执行内存查找。最后,带比例的内存类型可以通过左移来计算偏移量。
In Table 1, the notation
x0indicates the value stored in 64-bit registerx0, whereasw3indicates a 32-bit value stored in component registerw3. The operand[x0]indicates that the value insidex0should be treated as an address, and to dereference (look up) the value at that address. Therefore, the operand[x0]corresponds to *(0x804) or the value 0xCA. An operation on a 32-bit register can be combined with a 64-bit register using the sign-extend word (SXTW) instruction. So,[x0, w3, SXTW]sign extendsw3into a 64-bit value before adding it tox0and performing a memory lookup. Lastly, scaled memory types enable the calculation of offsets through the use of a left shift.
在继续之前,有几点重要说明。尽管表 1 列出了许多合法的操作数形式,但并不是所有形式在所有情况下都可以互换使用。
A few important notes before continuing. Although Table 1 shows many valid operand forms, not all forms can be used interchangeably in all circumstances.
具体来说:
Specifically:
- 不能直接对内存中的数据进行读写运算;ARM 遵循加载/存储(load/store)模型,要求数据在寄存器中进行运算。因此,数据必须先被传送到寄存器才能参与运算,运算完成后再传送回内存。
- Data cannot be read or written to memory directly; instead, ARM follows a load/store model, which requires data to be operated on in registers. Thus, data must be transferred to registers before being operated on, and transferred back to memory after the operations are complete.
- 指令的目标部分必须始终是寄存器。
- The destination component of an instruction must always be a register.
表 1 是供参考的;不过,理解关键的操作数形式会帮助读者更快地读懂汇编语言。
Table 1 is provided as a reference; however, understanding key operand forms will help improve the reader’s speed in parsing assembly language.